Terraform で google_api_gateway_api_config に api_config_id を設定すると再作成時に罠がある

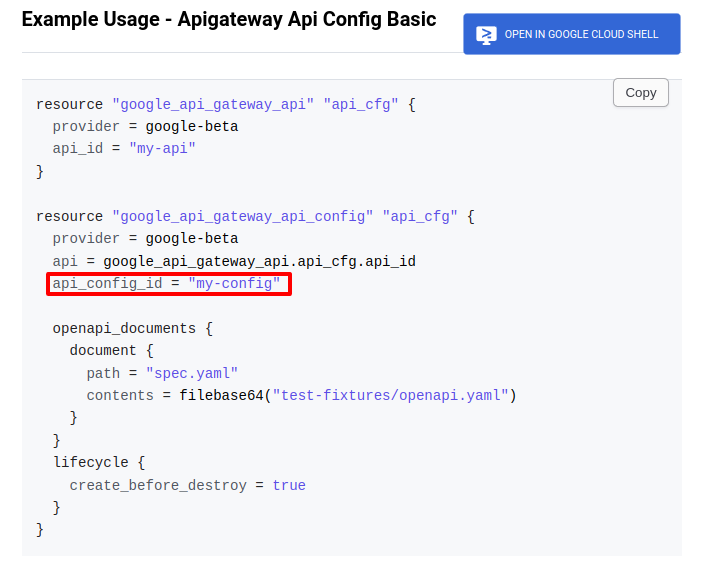
まとめ Terraform で google_api_gateway_api_config に api_config_id は設定しない 以下詳細 以下のように api_config_id を設定すると、再作成時にエラーが発生する resource "google_api_gateway_api_config" "default" { project = var.project_id provider = google-beta api = google_api_gateway_api.default.api_id api_config_id = "${var.env}-${var.service}-api-config" openapi_documents { document { path = "openapi.yaml" contents = base64encode(templatefile("${path.module}/openapi.yaml", { title = "${var.env} ${var.service} API" description = "This is the API for ${var.env} ${var.service}" version = "1.0.0" managed_service = google_api_gateway_api.default.managed_service func_url = google_cloud_run_service.default.status[0].url })) } } lifecycle { create_before_destroy = true } } │ Error: Error creating ApiConfig: googleapi: Error 409: Resource 'projects/{project_id}/locations/global/apis/{api_id}/configs/{api_config_name}' already exists │ Details: │ [ │ { │ "@type": "type.googleapis.com/google.rpc.ResourceInfo", │ "resourceName": "projects/{project_id}/locations/global/apis/{api_id}/configs/{api_config_name}" │ } │ ] 一見、create_before_destroy = true が指定されているので、新しいリソースを作成してから古いリソースを削除するように見えるが、 実際には api_config_id が変更されていないため、新しいリソースを作成することができない 省略した場合はタイムスタンプベースでIDが振られている… terraform-YYYYMMDDHHMMSS000000000001-xxxxxxxxxxxxx
2024-11-15 ·  2024-11-15 · 1 分 · 108 文字

GCP ApiGateway + CloudRun で CORS を設定する

構成 GCP ApiGateway -> CloudRun ApiGateway で OpenAPI yaml を定義している 1. OpenAPI yaml で x-google-endpoints に allowCors: True を設定して、バックエンドでCORSリクエストを処理する x-google-endpoints: - name: ${managed_service} allowCors: True # バックエンドでCORSリクエストを処理する 2. CloudRun で OPTIONS メソッドを設定する // 以下のように cors ミドルウェアを挟む http.HandleFunc("/example", cors(user.Handler)) // 定義はこんな感じ func cors(next http.HandlerFunc) http.HandlerFunc { return func(w http.ResponseWriter, r *http.Request) { if r.Method == "OPTIONS" { slog.Info("==> Reply OPTIONS Request", "status", http.StatusNoContent) w.Header().Set("Access-Control-Allow-Origin", "*") w.Header().Set("Access-Control-Allow-Methods", "GET, POST, PUT, PATCH, DELETE, OPTIONS") w.Header().Set("Access-Control-Allow-Headers", "DNT,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,Range,Authorization") w.Header().Set("Access-Control-Expose-Headers", "Content-Length,Content-Range") w.Header().Set("Access-Control-Max-Age", "1728000") // 20 days: reduce preflight requests w.WriteHeader(http.StatusNoContent) // 204 return } next.ServeHTTP(w, r) } } Refs Endpoints の CORS サポートを有効にする | Cloud Endpoints with OpenAPI | Google Cloud

2024-11-15 ·  2024-11-15 · 1 分 · 105 文字

terraform + GitHub Actions + ECR + Lambda + ApiGateway + OpenAPI 調査したのでメモ

はじめに 色々調べたのでメモ.. 以下詳細 Terraform で Lambdaも管理できないか? 最近やってるLambdaとAPI Gatewayの開発方法の話 tf, ecr, python, openapi TerraformでAPI Gateway + Lambdaの構成テンプレート #lambda - Qiita tf, NOT ecr, node, openapi TerraformでAmazon API Gatewayを構築する(基本編) #AWS - Qiita tf, NOT ecr, openapi LambdaをカスタムDockerランタイムで開発する方法 | フューチャー技術ブログ コンテナイメージを更新した際に気をつけるポイントですが、latestタグのコンテナイメージを更新しても、 すぐにLambda関数の挙動には反映されません。一晩寝かしても古いイメージが参照されていました。 全く同じimage-uriのまま更新コマンドを実行することで即時反映できます。 TerraformでLambdaコンテナイメージを自動構築する #Docker - Qiita swagger ecr lambda apigateway codebuild aws_lambda_alias lambda version に対するエイリアス これに対するIgnore設定の記載など 【AWS Lambda】複数のLambda関数を1つのコンテナイメージにまとめる #AWS - Qiita entrypoint指定できる aws_lambda_function | Resources | hashicorp/aws | Terraform | Terraform Registry ここでいうhandler? Terraform で ApiGateway を作成する 【Terraform】Terraformで作るサーバレス構成(API Gateway、Lambda、DynamoDB) TerraformでAmazon API Gatewayを構築するサンプルコードを書いてみた #AWS - Qiita Terraform で API Gateway(REST API)を構築する | DevelopersIO How to Create API Gateway With Terraform and AWS Lambda Creating a Rest API in AWS API Gateway using Terraform and OpenAPI Swagger specification | by InovaOnlineSolutions | Medium ECR の Pros and Cons Cons AWS Lambda で Go ランタイムを使うのが良いと思っている理由 基本的にコンテナイメージより zip 形式の方が安く使える コンテナイメージとカスタムランタイムは Lambda 関数の初期化時にも課金が発生する ...

2024-02-15 ·  2024-08-01 · 1 分 · 204 文字

Serverless で ApiGw のロギングいれようとして、`CloudWatch Logs role ARN must be set in account settings to enable logging` となったのでメモ

問題 Serverless Framework で、以下のようにロギング設定を追加して、以下エラーになった provider: # 省略 logs: restApi: accessLogging: false # Optional configuration which enables or disables access logging. Defaults to true. executionLogging: true # Optional configuration which enables or disables execution logging. Defaults to true. level: ERROR # Optional configuration which specifies the log level to use for execution logging. May be set to either INFO or ERROR. fullExecutionData: false # Optional configuration which specifies whether or not to log full requests/responses for execution logging. Defaults to true. CloudWatch Logs role ARN must be set in account settings to enable logging ...

2023-02-13 ·  2023-04-24 · 1 分 · 130 文字

ApiGatewayのログを ServerlessFramework で設定したい

要件としては、ApiGateway <=> Lambda の統合設定条件配下にて、 Lambdaからの応答結果が6MBを超えた場合に以下のようなログが出力される Lambda execution failed with status 200 due to customer function error: body size is too long. Lambda request id: XXXX-XXXX... これに対して、ServerlessFramework でログ設定を行いたい 参考 Serverless.yml Reference Enhancements for API Gateway REST API log setup Serverless complains about “Rest API id could not be resolved.” ApiGateway ステージ ログ/トレース の設定と動作 IAM Policy作成含め以下の設定だけで作成される provider: logs: restApi: accessLogging: false # Optional configuration which enables or disables access logging. Defaults to true. executionLogging: true # Optional configuration which enables or disables execution logging. Defaults to true. level: ERROR # Optional configuration which specifies the log level to use for execution logging. May be set to either INFO or ERROR. fullExecutionData: false # Optional configuration which specifies whether or not to log full requests/responses for execution logging. Defaults to true. CloudWatch ログを有効化(INFO/ERROR等の選択) API-Gateway-Execution-Logs_[APIID]/[stage] という形式でロググループが作成される ここに body size too long のログがでる ERROR のみで指定しないとリクエストが多い場合すぐ埋もれる。。 リクエスト/レスポンスをすべてログ /aws/api-gateway/[serviceName]-[stage] ロググループ アクセスカスタムログ /aws/api-gateway/[serviceName]-[stage] ロググループ format: で指定できる

2019-11-11 ·  2019-11-11 · 1 分 · 148 文字